In today’s increasingly complex regulatory landscape, the AML annual compliance report stands as a cornerstone of anti-money laundering program effectiveness. Financial institutions, fintech firms, and designated non-financial businesses and professions (DNFBPs) are required to produce this document annually to demonstrate adherence to national and international AML standards. Beyond mere regulatory tick-box exercise, a well-crafted report serves as a strategic tool for risk identification, internal accountability, and continuous improvement of compliance frameworks. This article provides an in-depth exploration of the AML annual compliance report, breaking down its essential elements, best practices, and common challenges, while offering actionable insights for compliance professionals seeking to elevate their reporting standards.
Understanding the AML Annual Compliance Report
Regulatory Framework and Objectives
The production of an AML annual compliance report is mandated under various jurisdictional statutes, including the Bank Secrecy Act (BSA) in the United States, the Proceeds of Crime (Money Laundering) and Terrorist Financing Act (PCMLTFA) in Canada, and the European Union’s Fifth Anti-Money Laundering Directive (5AMLD/6AMLD). While specific requirements vary, the overarching objective remains consistent: to provide regulators and senior management with a transparent snapshot of the institution’s AML posture over the preceding twelve months. This includes evaluating the design and operating effectiveness of internal controls, assessing the adequacy of customer due diligence (CDD) procedures, and documenting the outcomes of transaction monitoring and suspicious activity reporting (SAR).
Core Purpose and Stakeholder Expectations
Stakeholders ranging from board members and internal audit teams to external regulators and auditors rely on the AML annual compliance report to gauge risk exposure and compliance maturity. For executive leadership, the report offers a high-level view of resource allocation, training efficacy, and emerging threat trends. Regulators use it to assess compliance gaps, enforce corrective actions, and determine the need for supervisory interventions. Internally, the report fuels continuous improvement cycles, highlighting successes, pinpointing deficiencies, and guiding strategic investment in technology, personnel, and training.
Key Components of an Effective AML Annual Compliance Report
Risk Assessment and Customer Due Diligence
A robust AML annual compliance report begins with a comprehensive risk assessment that reflects the institution’s unique customer profile, geographic footprint, and product offerings. This section should detail the methodology used to categorize customers into risk tiers, the frequency of CDD updates, and any enhancements applied to high-risk accounts. Documentation of risk-based decision-making not only satisfies regulatory scrutiny but also ensures that resources are directed proportionally toward the areas of greatest vulnerability.
Transaction Monitoring and Suspicious Activity Reporting
The heart of any AML program lies in its ability to detect and report illicit activity. This subsection of the AML annual compliance report should quantify the volume of transactions screened, the number of alerts generated, and the disposition of those alerts—specifically how many were closed as false positives versus how many were escalated to SAR filings. Metrics such as detection rate, time-to-resolution, and SAR filing timeliness provide concrete evidence of the program’s operational effectiveness and its alignment with regulatory expectations.
Training and Awareness Programs
Human capital remains a critical line of defense against money laundering. The report should outline the training curriculum delivered to staff across all levels, including initial onboarding, annual refresher courses, and specialized training for frontline, middle-office, and risk-management personnel. Attendance records, assessment results, and any identified knowledge gaps should be included to demonstrate the program’s comprehensiveness and the institution’s commitment to cultivating a culture of compliance.
Independent Review and Audit Findings
Regular independent testing, whether conducted by internal audit or external consultants, provides an objective assessment of the AML program’s design and operating effectiveness. This section of the AML annual compliance report should summarize audit findings, remediation status, and any persistent deficiencies requiring management attention. Transparent disclosure of audit outcomes reinforces stakeholder confidence and underscores the institution’s dedication to maintaining an resilient compliance framework.
Best Practices for Drafting and Submitting Your AML Annual Compliance Report
Internal Audit and Review Mechanisms
Establishing a rigorous internal review process is essential for producing a credible AML annual compliance report. Institutions should implement a standardized checklist that aligns with regulatory guidelines and internal policies. This checklist should cover every major component of the AML program, from policy documentation and risk assessment to SAR filing procedures and record-keeping practices. By internalizing the review process, compliance teams can identify and rectify discrepancies before external scrutiny, thereby reducing the risk of regulatory findings.
Documentation and Record-Keeping
Thorough documentation is the backbone of an defensible AML annual compliance report. All policies, procedures, risk assessments, training records, SAR filings, and investigation outcomes must be systematically archived and easily retrievable. Digital compliance management platforms can streamline this process, ensuring version control, audit trails, and rapid report generation. Moreover, maintaining a centralized repository of evidence not only facilitates annual reporting but also supports responses to regulatory inquiries, examinations, and legal proceedings.
Common Pitfalls and How to Avoid Them
Incomplete Risk Assessments
One of the most frequently observed shortcomings in an AML annual compliance report is a risk assessment that is either outdated, overly generic, or misaligned with the institution’s current business model. Regulators expect risk assessments to be dynamic, reflecting changes in customer behavior, product innovation, and evolving threat landscapes. To mitigate this, institutions should conduct risk assessments at least annually, with interim updates triggered by significant operational changes. Incorporating quantitative data, such as customer segmentation analytics and geographic risk scores, enhances the assessment’s precision and relevance.
Outdated Policies and Procedures
Stagnant policies and procedures can undermine the credibility of the AML annual compliance report and expose the institution to compliance gaps. Policies must be reviewed and revised regularly to incorporate regulatory updates, lessons learned from internal incidents, and best practices from industry peers. A formal policy change management process—encompassing impact analysis, stakeholder consultation, and approval workflows—ensures that modifications are systematically implemented and documented.
Inconsistent SAR Filing Practices
Timeliness and quality of suspicious activity reports are critical metrics evaluated within the AML annual compliance report. Delays in filing, incomplete information, or duplicate submissions can attract regulatory penalties and damage the institution’s reputation. Establishing clear internal SLAs for SAR preparation, review, and submission, coupled with automated tracking systems, helps maintain consistency and accuracy. Regular training on SAR criteria and filing procedures further reinforces adherence to best practices.
Leveraging Technology for Enhanced Reporting
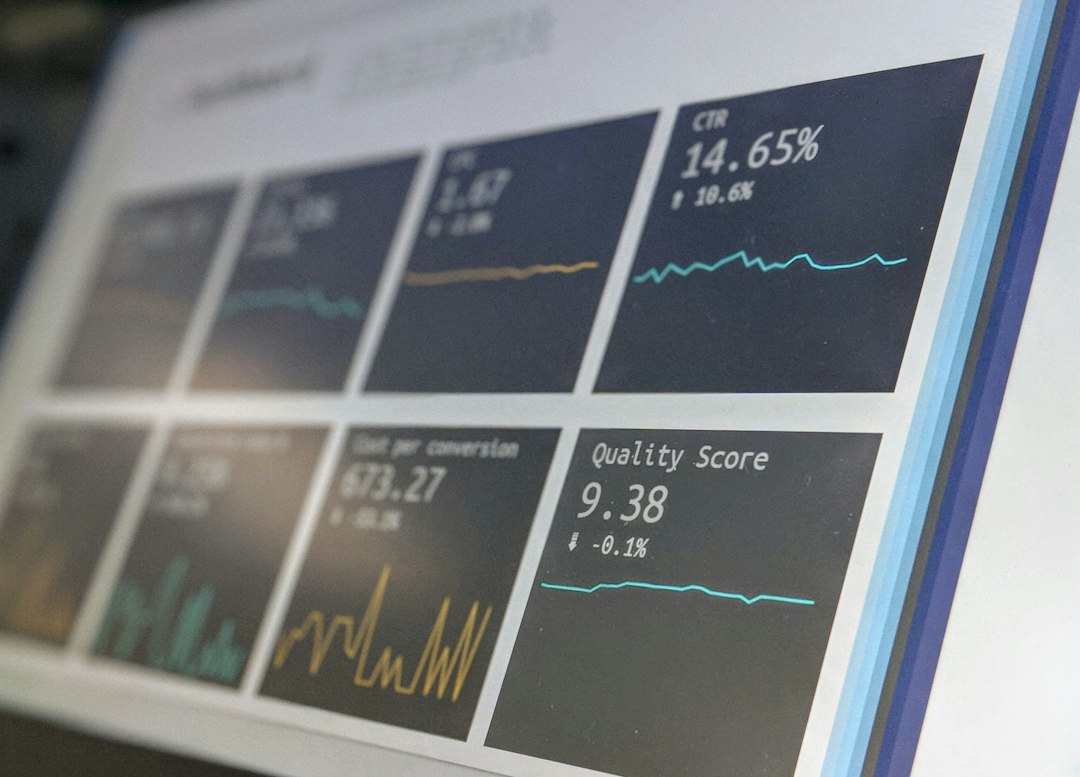
Advancements in regtech and compliance analytics are transforming the way institutions approach the AML annual compliance report. Machine learning algorithms can refine transaction monitoring accuracy, reducing false-positive rates and freeing analysts to focus on genuine threats. Blockchain-based immutable ledgers offer transparent audit trails for CDD documentation and transaction histories. Additionally, integrated compliance platforms enable real-time dashboards, automated report generation, and seamless data integration across disparate systems. Embracing these technologies not only improves reporting efficiency but also elevates the overall strategic value of the AML function.
Future Trends Shaping the AML Annual Compliance Report
The regulatory environment surrounding anti-money laundering is in a state of constant flux, and the AML annual compliance report must evolve accordingly. Emerging trends include increased emphasis on beneficial ownership transparency, greater coordination between domestic and international regulators, and the integration of virtual asset service providers (VASPs) into traditional AML frameworks. Furthermore, the rise of real-time payment systems and cross-border digital assets necessitates more agile monitoring and reporting mechanisms. Institutions that proactively adapt their reporting practices to these trends will not only maintain compliance but also gain a competitive edge in risk management and stakeholder trust.
In summary, the AML annual compliance report is far more than a regulatory requirement; it is a strategic artifact that reflects an institution’s commitment to integrity, risk awareness, and continuous improvement. By understanding its core components, adhering to best practices, and leveraging technological innovations, compliance professionals can produce reports that satisfy regulators, inform leadership, and strengthen the organization’s overall AML posture. As financial crime tactics grow more sophisticated, a robust and well-executed annual compliance report remains the most effective defense an institution can deploy.
Is your organization’s AML annual compliance report ready for the next regulatory examination? Investing in a systematic, data-driven approach to report preparation today can save significant time, resources, and reputational risk tomorrow.
The AML annual compliance report: A Strategic Lens on Crypto Market Accountability
As James Richardson, Senior Crypto Market Analyst with over a decade of experience tracking digital asset trajectories, the emergence of structured regulatory frameworks like the AML annual compliance report signals a maturation phase for the broader cryptocurrency ecosystem. In an industry historically defined by rapid innovation outpacing oversight, such reports serve as critical anchor points, translating on-chain activity into actionable compliance metrics. The systematic documentation of anti-money laundering controls not only protects institutional partners but also provides retail investors with a measurable degree of confidence in market integrity.
From a practical standpoint, the AML annual compliance report offers more than a checkbox exercise; it encapsulates the efficacy of know-your-customer protocols, transaction monitoring thresholds, and risk-tiered categorization across major exchanges and custodial services. In my analyses, I have observed that projects maintaining rigorous, transparent compliance postures tend to exhibit lower volatility premiums and faster adoption curves among venture capital firms. Conversely, gaps in reporting often correlate with heightened regulatory scrutiny, which can suppress liquidity and deter long-term capital allocation. The report's granular data points allow analysts like myself to triangulate risk-adjusted valuation models with greater precision.
Looking ahead, the integration of real-time analytics with traditional AML reporting frameworks will likely redefine how market participants assess systemic risk. As decentralized finance protocols and layer-2 solutions expand their footprints, the principles embedded in the AML annual compliance report must evolve to encompass cross-chain interoperability and smart contract audit standards. For now, however, it remains an indispensable benchmark: a bridge between the ethos of financial sovereignty and the realities of global regulatory expectations. Stakeholders who treat this document as a strategic asset rather than a bureaucratic formality will be best positioned to navigate the next wave of institutional capital inflow.